Domain, Web & API Shield
SecureDomain and WebShield inspect DNS, web traffic, APIs, and volumetric attacks before they reach your firewall or application servers.
Home / AuraLink with ProtectionGrid
AuraLink with ProtectionGrid.
A 2U rack appliance powered by dual Identiqa Aura processors that defends every external entry point and locks snapshots at the storage layer. Even stolen domain or backup administrator credentials can't overwrite or purge your recovery copy.
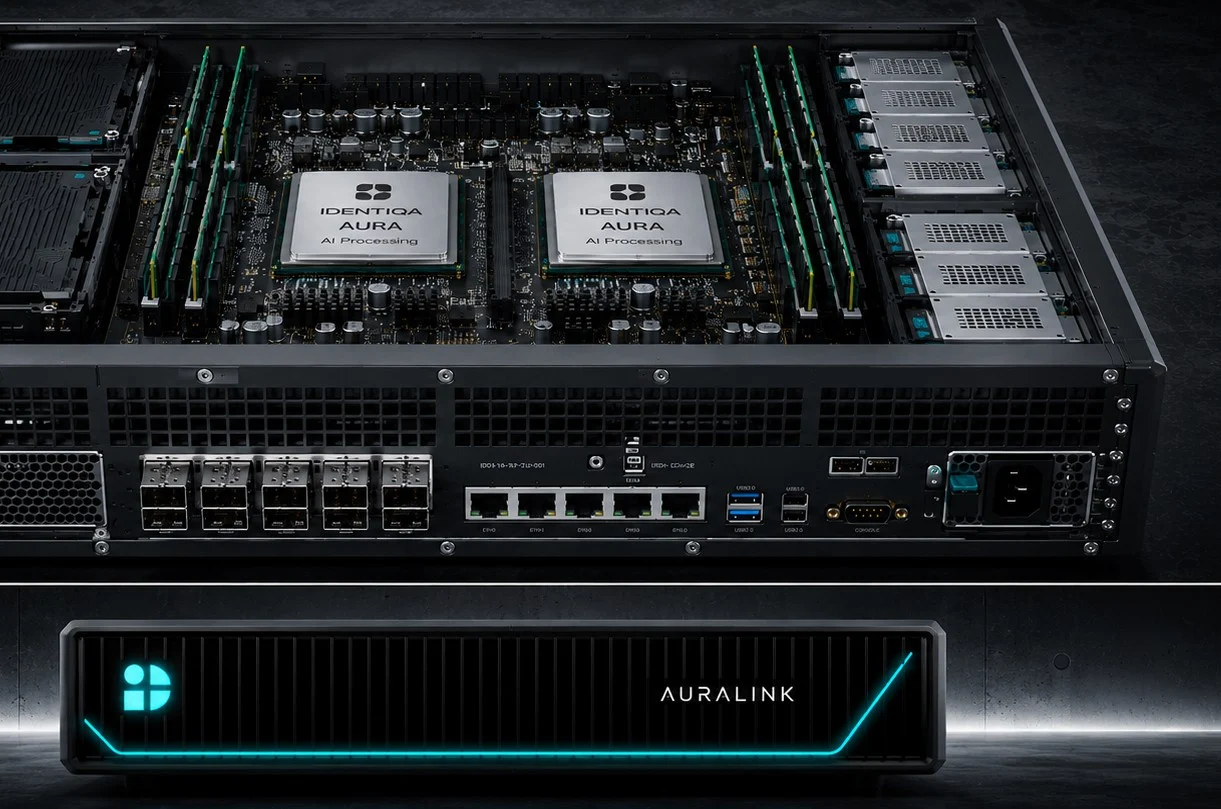
AuraLink deploys alongside your existing firewall: six integrated protection layers and hardware-locked backups in one 2U chassis.
SecureDomain and WebShield inspect DNS, web traffic, APIs, and volumetric attacks before they reach your firewall or application servers.
MailShield blocks phishing and malicious payloads, HybridMail keeps mail alive during primary outages, and AppShield + WebAuth replace legacy VPNs.
Snapshots are cryptographically locked on the AuraLink appliance and replicated to the Identiqa Cloud. No admin account can alter them during retention.
In 94 per cent of ransomware attacks, adversaries attempt to destroy or encrypt backups, and they succeed in 57 per cent of those attempts (Sophos 2024). AuraLink with ProtectionGrid locks every backup snapshot cryptographically on the local appliance and in the Identiqa Cloud. During its retention period, no user, script, or compromised administrator account can overwrite or delete it because immutability is enforced by the storage layer itself.
Conventional backup software fails during ransomware incidents because its retention settings can be altered by a compromised domain or backup administrator. AuraLink enforces immutability inside the storage subsystem itself: once a snapshot is written and replicated to the Identiqa Cloud, the storage controller rejects any modify or delete instruction until the cryptographic retention timer expires.
Across the 2U appliance and the Identiqa Cloud, six specialized modules inspect traffic inline: SecureDomain protects DNS integrity, WebShield filters web applications and APIs while absorbing DDoS floods, MailShield strips phishing and malicious payloads, HybridMail keeps mail flowing if your primary provider goes down, AppShield replaces legacy VPNs with zero-trust application access, and WebAuth protects sign-in for your own workforce with phishing-resistant authentication; it does not verify consumer identities, and Identiqa is not a KYC vendor.
AuraLink is engineered to isolate a spreading breach at the network edge without waiting for an analyst to read a dashboard. Sub-minute containment is our engineering design target, not a blanket marketing SLA.
We size Identiqa to your infrastructure and sites. Buy directly through Identiqa or on your existing agreement with Amazon Web Services, Google Cloud, or Microsoft Azure.
See how AuraCore secures your serversTrue immutability must be enforced by the storage subsystem rather than a toggle in backup administration software. Identiqa locks every snapshot cryptographically at the storage layer of the 2U AuraLink appliance and in the Identiqa Cloud, ensuring that even stolen root or domain administrator credentials cannot modify or delete the copy during its retention window.
Traditional firewalls govern ports and IP flows but don't secure DNS integrity, mail payloads, VPN-less application access, phishing-resistant workforce sign-in, or storage-locked backups. Identiqa's 2U AuraLink appliance deploys alongside your existing firewall in the rack to close those exact six gaps.
By breaking the attack chain at two decisive points: Identiqa ProtectionGrid blocks initial intrusion and lateral command traffic at the network edge while holding a hardware-locked backup copy on the AuraLink appliance so your organisation can restore cleanly without paying a ransom.